Modern businesses need to release software faster while protecting applications, infrastructure, and customer data from evolving cyber threats. Traditional security models that perform checks only at the end of the development cycle create delays, increase risks, and slow innovation.
At OpsBee, we deliver AI-powered DevSecOps Services that integrate security into every stage of the software delivery lifecycle—from code development and CI/CD pipelines to cloud infrastructure and production environments. Through security automation, continuous testing, cloud-native security, and proactive monitoring, we help businesses accelerate software delivery, reduce vulnerabilities, and strengthen compliance.
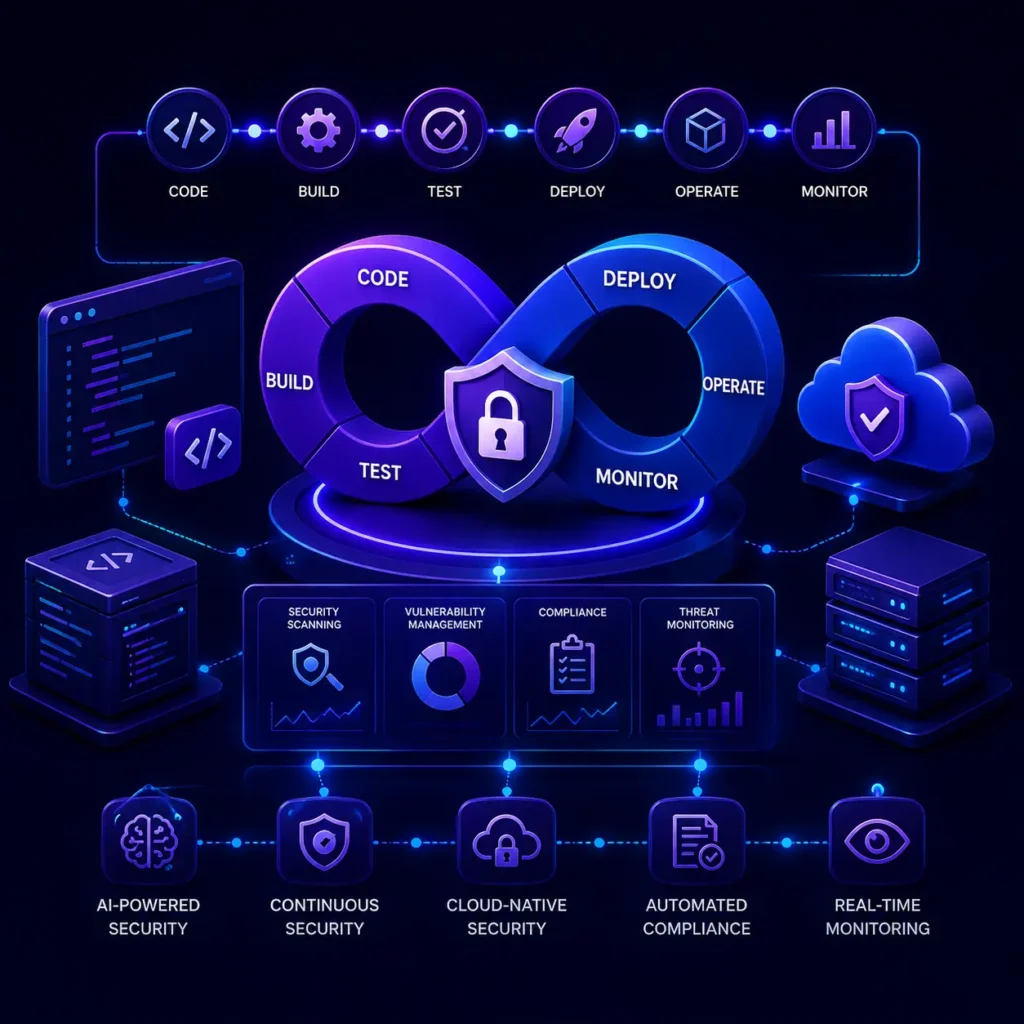
Partner with OpsBee to build secure and scalable software delivery pipelines that integrate security across development, operations, and cloud environments.
Design and implement automated CI/CD pipelines with integrated security controls that ensure every release follows security best practices while accelerating software delivery.
Automate security testing, policy enforcement, infrastructure provisioning, and deployment workflows to eliminate manual errors and improve operational efficiency.
Implement SAST, DAST, dependency scanning, container scanning, and code quality checks to identify vulnerabilities early and reduce security risks throughout the development lifecycle.
Secure Docker containers, Kubernetes clusters, container registries, and runtime environments through policy enforcement, image scanning, and runtime protection.
Implement IAM policies, security baselines, compliance automation, and cloud security monitoring to strengthen security posture across multi-cloud environments.
Enable proactive threat detection through continuous monitoring, log analysis, intelligent alerting, and security event management across applications and infrastructure.
Partner with OpsBee to build secure and scalable software delivery pipelines that integrate security across development, operations, and cloud environments.
Design and implement automated CI/CD pipelines with integrated security controls that ensure every release follows security best practices while accelerating software delivery.
Automate security testing, policy enforcement, infrastructure provisioning, and deployment workflows to eliminate manual errors and improve operational efficiency.
Implement SAST, DAST, dependency scanning, container scanning, and code quality checks to identify vulnerabilities early and reduce security risks throughout the development lifecycle.
Secure Docker containers, Kubernetes clusters, container registries, and runtime environments through policy enforcement, image scanning, and runtime protection.
Implement IAM policies, security baselines, compliance automation, and cloud security monitoring to strengthen security posture across multi-cloud environments.
Enable proactive threat detection through continuous monitoring, log analysis, intelligent alerting, and security event management across applications and infrastructure.
At OpsBee, we combine DevOps automation, security-first practices, and cloud-native technologies to build secure, scalable, and high-performing software delivery pipelines. Our DevSecOps solutions are designed to accelerate releases, reduce security risks, and help organizations innovate with confidence.
Our DevSecOps Services Help Organizations:
Accelerate software delivery with secure and automated CI/CD pipelines.
Reduce application and infrastructure vulnerabilities through continuous security integration.
Improve compliance and governance with automated policy enforcement and security controls.
Enhance visibility with proactive monitoring, threat detection, and security analytics.
Strengthen cloud and Kubernetes security across modern distributed environments.
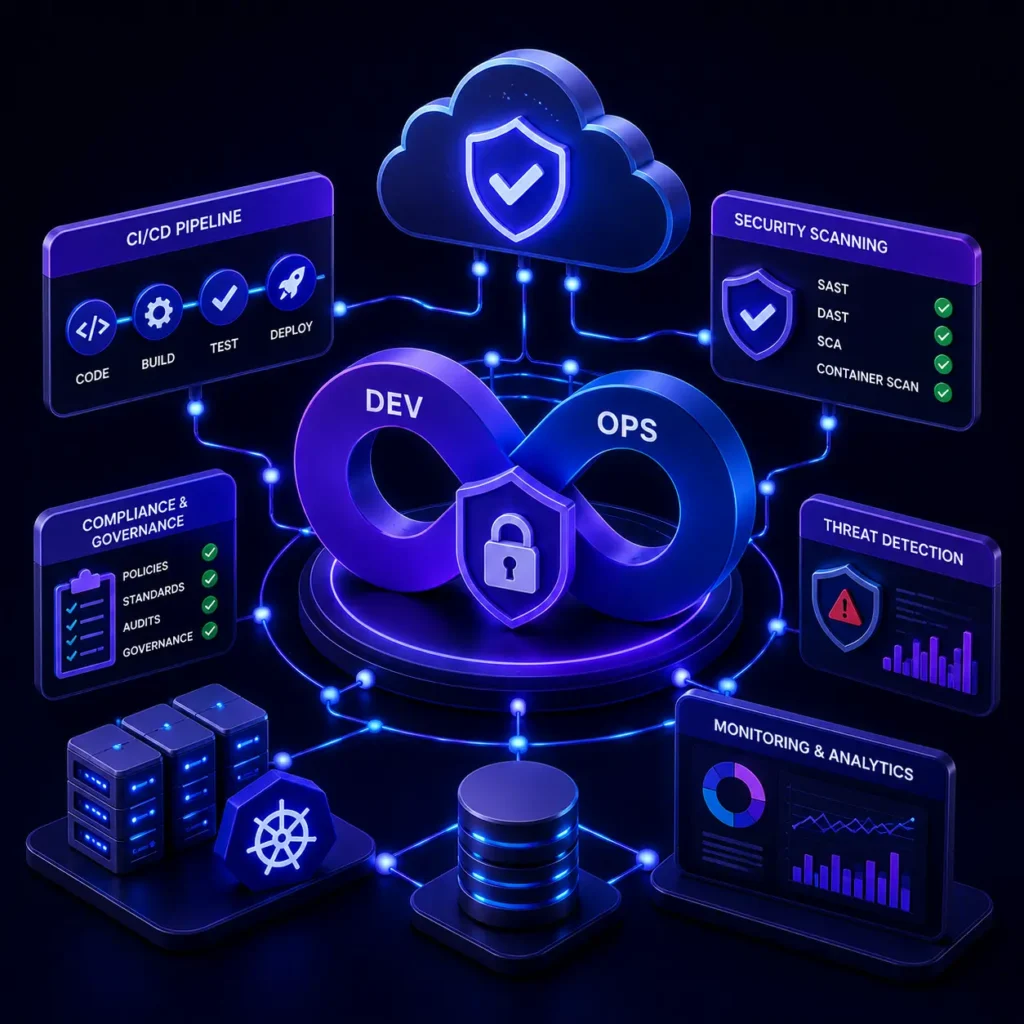
At OpsBee, we combine DevOps automation, security-first practices, and cloud-native technologies to build secure, scalable, and high-performing software delivery pipelines. Our DevSecOps solutions are designed to accelerate releases, reduce security risks, and help organizations innovate with confidence.
Our DevSecOps Services Help Organizations:
Accelerate software delivery with secure and automated CI/CD pipelines.
Reduce application and infrastructure vulnerabilities through continuous security integration.
Improve compliance and governance with automated policy enforcement and security controls.
Enhance visibility with proactive monitoring, threat detection, and security analytics.
Strengthen cloud and Kubernetes security across modern distributed environments.
Build scalable DevSecOps ecosystems that support long-term business growth.
Selecting the right DevSecOps tools and security frameworks depends on application architecture, compliance requirements, deployment workflows, and business objectives. OpsBee helps organizations implement modern DevSecOps solutions that integrate security seamlessly across development, operations, and cloud environments.
Jenkins, GitLab CI, GitHub Actions, and Azure DevOps enable automated build, testing, security scanning, and deployment workflows that accelerate software delivery while maintaining security, consistency, and operational reliability.
SonarQube, Snyk, OWASP ZAP, and Trivy provide automated code analysis, vulnerability scanning, dependency checks, and container security to identify and remediate risks early in the software development lifecycle.
Docker, Kubernetes, Kyverno, Falco, and Aqua Security help secure containerized applications through policy enforcement, runtime protection, image scanning, and Kubernetes security best practices.
AWS Security Hub, Microsoft Defender for Cloud, Google Security Command Center, and IAM solutions provide continuous monitoring, threat detection, identity and access management, and compliance automation across multi-cloud environments.
Partner with OpsBee for advanced DevSecOps Services that integrate security into every stage of development and operations. We help organizations automate CI/CD pipelines, strengthen application security, secure cloud environments, and build resilient cloud-native architectures designed for long-term growth.
Have questions about DevSecOps implementation, CI/CD security, application security testing, Kubernetes security, or compliance automation? Explore some of the most common questions organizations ask before partnering with OpsBee.
DevSecOps Services integrate security into every stage of the software development lifecycle, enabling organizations to build, test, and deploy applications securely and efficiently.
DevSecOps automates security checks, reduces vulnerabilities, and enables faster, more reliable software releases.
We support tools such as SonarQube, Trivy, Snyk, OWASP ZAP, Jenkins, GitLab CI, GitHub Actions, Terraform, Kubernetes, and cloud-native security platforms.
Yes. We implement security best practices for Docker, Kubernetes, container registries, and runtime environments.
DevSecOps improves security, accelerates delivery, reduces compliance risks, and helps organizations build scalable and resilient software delivery pipelines.
OpsBee Technology stands as a trusted provider of IT Managed Services and Infrastructure Solutions, delivering reliable technology support and services across India.
Copyright © 2026 All Rights Reserved.